FD ISO 31004
FD ISO 31004

FD ISO 31004

February 2014
Published document Cancelled

Risk management - Guidance for the implementation of ISO 31000

ISO/TR 31004:2013 provides guidance for organizations on managing risk effectively by implementing ISO 31000:2009. It provides:a structured approach for organizations to transition their risk management arrangements in order to be consistent with ISO 31000, in a manner tailored to the characteristics of the organization;an explanation of the underlying concepts of ISO 31000;guidance on aspects of the principles and risk management framework that are described in ISO 31000.ISO/TR 31004:2013 can be used by any public, private or community enterprise, association, group or individual.ISO/TR 31004:2013 is not specific to any industry or sector, or to any particular type of risk, and can be applied to all activities and to all parts of organizations.

Main informations

Collections

National standards and national normative documents

Thematics

Management et performance, QSE, Sécurité, Développement durable et RSE

Publication date

February 2014

Number of pages

47 p.

Reference

FD ISO 31004

ICS Codes

03.100.01   Company organization and management in general

Classification index

X50-255

Print number

1

International kinship

ISO/TR 31004:2013
Sumary
Risk management - Guidance for the implementation of ISO 31000

ISO/TR 31004:2013 provides guidance for organizations on managing risk effectively by implementing ISO 31000:2009. It provides:

  • a structured approach for organizations to transition their risk management arrangements in order to be consistent with ISO 31000, in a manner tailored to the characteristics of the organization;
  • an explanation of the underlying concepts of ISO 31000;
  • guidance on aspects of the principles and risk management framework that are described in ISO 31000.

ISO/TR 31004:2013 can be used by any public, private or community enterprise, association, group or individual.

ISO/TR 31004:2013 is not specific to any industry or sector, or to any particular type of risk, and can be applied to all activities and to all parts of organizations.

Table of contents
  • Avant-propos
    iv
  • Introduction
    v
  • 1 Domaine d'application
    1
  • 2 Références normatives
    1
  • 3 Mise en oeuvre de l'ISO 31000
    1
  • 3.1 Généralités
    1
  • 3.2 Comment mettre en oeuvre l'ISO 31000
    2
  • 3.3 Intégration de l'ISO 31000 aux processus de management de l'organisme
    3
  • 3.4 Amélioration continue
    6
  • Annexe A (informative) Concepts et principes sous-jacents
    8
  • Annexe B (informative) Application des principes de l'ISO 31000
    11
  • Annexe C (informative) Comment exprimer mandat et engagement
    22
  • Annexe D (informative) Surveillance et revue
    26
  • Annexe E (informative) Intégration du management du risque à un système de management
    36
  • Bibliographie
    39
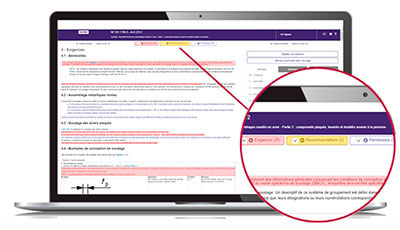
ZOOM ON ... the Requirements department

To comply with a standard, you need to quickly understand its issues in order to determine its impact on your activity.

The Requirements department helps you quickly locate within the normative text:

  • mandatory clauses to satisfy,
  • non-essential but useful clauses to know, such as permissions and recommendations.

The identification of these types of clauses is based on the document "ISO/IEC Directives, Part 2 - Principles and rules of structure and drafting of ISO documents" as well as on a constantly enriched list of verbal forms.

With Requirements, quickly access the main part of the normative text!


New: UPSELL service
Need to identify, monitor and decipher standards?