IEC 62443-3-2:2020
Security for industrial automation and control systems - Part 3-2: Security risk assessment for system design
IEC 62443-3-2:2020 establishes requirements for:• defining a system under consideration (SUC) for an industrial automation and control system (IACS);• partitioning the SUC into zones and conduits;• assessing risk for each zone and conduit;• establishing the target security level (SL-T) for each zone and conduit; and• documenting the security requirements.
IEC 62443-3-2:2020 establishes requirements for:
• defining a system under consideration (SUC) for an industrial automation and control system (IACS);
• partitioning the SUC into zones and conduits;
• assessing risk for each zone and conduit;
• establishing the target security level (SL-T) for each zone and conduit; and
• documenting the security requirements.
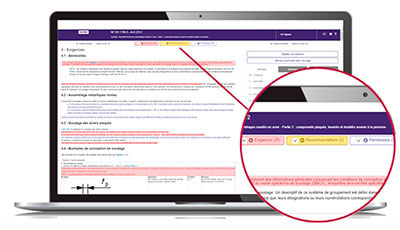
To comply with a standard, you need to quickly understand its issues in order to determine its impact on your activity.
The Requirements department helps you quickly locate within the normative text:
- mandatory clauses to satisfy,
- non-essential but useful clauses to know, such as permissions and recommendations.
The identification of these types of clauses is based on the document "ISO/IEC Directives, Part 2 - Principles and rules of structure and drafting of ISO documents" as well as on a constantly enriched list of verbal forms.
With Requirements, quickly access the main part of the normative text!

COBAZ is the simple and effective solution to meet the normative needs related to your activity, in France and abroad.
Available by subscription, CObaz is THE modular solution to compose according to your needs today and tomorrow. Quickly discover CObaz!
Request your free, no-obligation live demo
I discover COBAZ