IEC 80001-1:2021
IEC 80001-1:2021

IEC 80001-1:2021

September 2021
International standard Current

Application of risk management for IT-networks incorporating medical devices - Part 1: Safety, effectiveness and security in the implementation and use of connected medical devices or connected health software

IEC 80001-1:2021 specifies general requirements for ORGANIZATIONS in the application of RISK MANAGEMENT before, during and after the connection of a HEALTH IT SYSTEM within a HEALTH IT INFRASTRUCTURE, by addressing the KEY PROPERTIES of SAFETY, EFFECTIVENESS and SECURITY whilst engaging appropriate stakeholders.IEC 80001-1:2021 cancels and replaces the first edition published in 2010. This edition constitutes a technical revision.This edition includes the following significant technical changes with respect to the previous edition:a) structure changed to better align with ISO 31000;b) establishment of requirements for an ORGANIZATION in the application of RISK MANAGEMENT;c) communication of the value, intention and purpose of RISK MANAGEMENT through principles that support preservation of the KEY PROPERTIES during the implementation and use of connected HEALTH SOFTWARE and/or HEALTH IT SYSTEMS.

Main informations

Collections

International IEC standards

Publication date

September 2021

Number of pages

75 p.

Reference

IEC 80001-1:2021

ICS Codes

35.240.80   IT applications in health care technology
11.040.01   Medical equipment in general
Sumary
Application of risk management for IT-networks incorporating medical devices - Part 1: Safety, effectiveness and security in the implementation and use of connected medical devices or connected health software

IEC 80001-1:2021 specifies general requirements for ORGANIZATIONS in the application of RISK MANAGEMENT before, during and after the connection of a HEALTH IT SYSTEM within a HEALTH IT INFRASTRUCTURE, by addressing the KEY PROPERTIES of SAFETY, EFFECTIVENESS and SECURITY whilst engaging appropriate stakeholders.
IEC 80001-1:2021 cancels and replaces the first edition published in 2010. This edition constitutes a technical revision.
This edition includes the following significant technical changes with respect to the previous edition:
a) structure changed to better align with ISO 31000;
b) establishment of requirements for an ORGANIZATION in the application of RISK MANAGEMENT;
c) communication of the value, intention and purpose of RISK MANAGEMENT through principles that support preservation of the KEY PROPERTIES during the implementation and use of connected HEALTH SOFTWARE and/or HEALTH IT SYSTEMS.
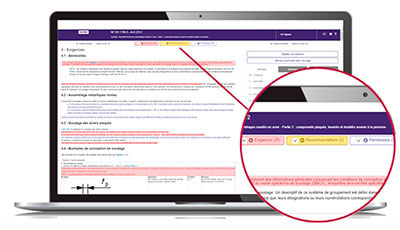
ZOOM ON ... the Requirements department

To comply with a standard, you need to quickly understand its issues in order to determine its impact on your activity.

The Requirements department helps you quickly locate within the normative text:

  • mandatory clauses to satisfy,
  • non-essential but useful clauses to know, such as permissions and recommendations.

The identification of these types of clauses is based on the document "ISO/IEC Directives, Part 2 - Principles and rules of structure and drafting of ISO documents" as well as on a constantly enriched list of verbal forms.

With Requirements, quickly access the main part of the normative text!


Need to identify, monitor and decipher standards?