ISO/IEC 27036-3:2023

ISO/IEC 27036-3:2023

June 2023
International standard Current

Cybersecurity - Supplier relationships - Part 3: Guidelines for hardware, software, and services supply chain security

This document provides guidance for product and service acquirers, as well as suppliers of hardware, software and services, regarding:a)    gaining visibility into and managing the information security risks caused by physically dispersed and multi-layered hardware, software, and services supply chains;b)    responding to risks stemming from this physically dispersed and multi-layered hardware, software, and services supply chain that can have an information security impact on the organizations using these products and services;c)    integrating information security processes and practices into the system and software life cycle processes, as described in ISO/IEC/IEEE 15288 and ISO/IEC/IEEE 12207, while supporting information security controls, as described in ISO/IEC 27002.This document does not include business continuity management/resiliency issues involved with the hardware, software, and services supply chain. ISO/IEC 27031 addresses information and communication technology readiness for business continuity.
View the extract
Main informations

Collections

International ISO standards
International IEC standards

Publication date

June 2023

Number of pages

35 p.

Reference

ISO/IEC 27036-3:2023

ICS Codes

35.030   IT Security

Print number

1
Sumary
Cybersecurity - Supplier relationships - Part 3: Guidelines for hardware, software, and services supply chain security

This document provides guidance for product and service acquirers, as well as suppliers of hardware, software and services, regarding:

a)    gaining visibility into and managing the information security risks caused by physically dispersed and multi-layered hardware, software, and services supply chains;

b)    responding to risks stemming from this physically dispersed and multi-layered hardware, software, and services supply chain that can have an information security impact on the organizations using these products and services;

c)    integrating information security processes and practices into the system and software life cycle processes, as described in ISO/IEC/IEEE 15288 and ISO/IEC/IEEE 12207, while supporting information security controls, as described in ISO/IEC 27002.

This document does not include business continuity management/resiliency issues involved with the hardware, software, and services supply chain. ISO/IEC 27031 addresses information and communication technology readiness for business continuity.
Replaced standards (1)
ISO/IEC 27036-3:2013
November 2013
International standard Cancelled
Information technology - Security techniques - Information security for supplier relationships - Part 3 : guidelines for information and communication technology supply chain security

ISO/IEC 27036-3:2013 provides product and service acquirers and suppliers in the information and communication technology (ICT) supply chain with guidance on: gaining visibility into and managing the information security risks caused by physically dispersed and multi-layered ICT supply chains; responding to risks stemming from the global ICT supply chain to ICT products and services that can have an information security impact on the organizations using these products and services. These risks can be related to organizational as well as technical aspects (e.g. insertion of malicious code or presence of the counterfeit information technology (IT) products); integrating information security processes and practices into the system and software lifecycle processes, described in ISO/IEC 15288 and ISO/IEC 12207, while supporting information security controls, described in ISO/IEC 27002. ISO/IEC 27036-3:2013 does not include business continuity management/resiliency issues involved with the ICT supply chain. ISO/IEC 27031 addresses business continuity.

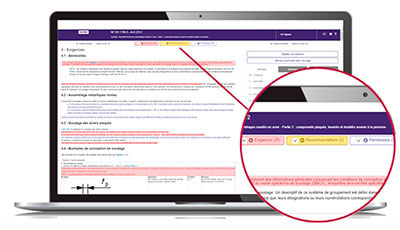
ZOOM ON ... the Requirements department

To comply with a standard, you need to quickly understand its issues in order to determine its impact on your activity.

The Requirements department helps you quickly locate within the normative text:

  • mandatory clauses to satisfy,
  • non-essential but useful clauses to know, such as permissions and recommendations.

The identification of these types of clauses is based on the document "ISO/IEC Directives, Part 2 - Principles and rules of structure and drafting of ISO documents" as well as on a constantly enriched list of verbal forms.

With Requirements, quickly access the main part of the normative text!


Need to identify, monitor and decipher standards?