ISO/IEC 27701:2025
ISO/IEC 27701:2025

ISO/IEC 27701:2025

October 2025
International standard Current

Information security, cybersecurity and privacy protection - Privacy information management systems - Requirements and guidance

This document specifies requirements for establishing, implementing, maintaining and continually improving a privacy information management system (PIMS).Guidance is also provided to assist in the implementation of the requirements in this document.This document is intended for personally identifiable information (PII) controllers and PII processors holding responsibility and accountability for PII processing.This document is applicable to all types and sizes of organizations, including public and private companies, government entities and not-for-profit organizations.

View the extract
Main informations

Collections

International ISO standards
International IEC standards

Publication date

October 2025

Number of pages

71 p.

Reference

ISO/IEC 27701:2025

ICS Codes

35.030   IT Security

Print number

1
Sumary
Information security, cybersecurity and privacy protection - Privacy information management systems - Requirements and guidance

This document specifies requirements for establishing, implementing, maintaining and continually improving a privacy information management system (PIMS).

Guidance is also provided to assist in the implementation of the requirements in this document.

This document is intended for personally identifiable information (PII) controllers and PII processors holding responsibility and accountability for PII processing.

This document is applicable to all types and sizes of organizations, including public and private companies, government entities and not-for-profit organizations.

Replaced standards (1)
ISO/IEC 27701:2019
ISO/IEC 27701:2019
August 2019
International standard Cancelled
Security techniques - Extension to ISO/IEC 27001 and ISO/IEC 27002 for privacy information management - Requirements and guidelines

This document specifies requirements and provides guidance for establishing, implementing, maintaining and continually improving a Privacy Information Management System (PIMS) in the form of an extension to ISO/IEC 27001 and ISO/IEC 27002 for privacy management within the context of the organization. This document specifies PIMS-related requirements and provides guidance for PII controllers and PII processors holding responsibility and accountability for PII processing. This document is applicable to all types and sizes of organizations, including public and private companies, government entities and not-for-profit organizations, which are PII controllers and/or PII processors processing PII within an ISMS.

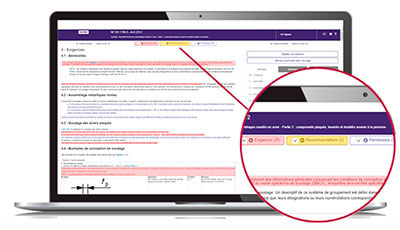
ZOOM ON ... the Requirements department

To comply with a standard, you need to quickly understand its issues in order to determine its impact on your activity.

The Requirements department helps you quickly locate within the normative text:

  • mandatory clauses to satisfy,
  • non-essential but useful clauses to know, such as permissions and recommendations.

The identification of these types of clauses is based on the document "ISO/IEC Directives, Part 2 - Principles and rules of structure and drafting of ISO documents" as well as on a constantly enriched list of verbal forms.

With Requirements, quickly access the main part of the normative text!


What is the Redline format?
Need to identify, monitor and decipher standards?