NF EN ISO/IEC 27701
NF EN ISO/IEC 27701

NF EN ISO/IEC 27701

September 2021
Standard Cancelled

Security techniques - Extension to ISO/IEC 27001 and ISO/IEC 27002 for privacy information management - Requirements and guidelines (ISO/IEC 27701:2019)

Main informations

Collections

National standards and national normative documents

Publication date

September 2021

Number of pages

87 p.

Reference

NF EN ISO/IEC 27701

ICS Codes

35.030   IT Security

Print number

1

International kinship

ISO/IEC 27701:2019

European kinship

EN ISO/IEC 27701:2021
Replaced standards (1)
NF ISO/IEC 27701
NF ISO/IEC 27701
October 2020
Standard Cancelled
Security techniques - Extension to ISO/IEC 27001 and ISO/IEC 27002 for privacy information management - Requirements and guidelines

This document specifies requirements and provides guidance for establishing, implementing, maintaining and continually improving a Privacy Information Management System (PIMS) in the form of an extension to ISO/IEC 27001 and ISO/IEC 27002 for privacy management within the context of the organization. This document specifies PIMS-related requirements and provides guidance for PII controllers and PII processors holding responsibility and accountability for PII processing. This document is applicable to all types and sizes of organizations, including public and private companies, government entities and not-for-profit organizations, which are PII controllers and/or PII processors processing PII within an ISMS.

Standard replaced by (1)
NF EN ISO/IEC 27701
NF EN ISO/IEC 27701
October 2025
Standard Current
Information security, cybersecurity and privacy protection - Privacy information management systems - Requirements and guidance

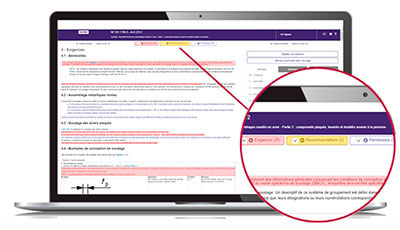
ZOOM ON ... the Requirements department

To comply with a standard, you need to quickly understand its issues in order to determine its impact on your activity.

The Requirements department helps you quickly locate within the normative text:

  • mandatory clauses to satisfy,
  • non-essential but useful clauses to know, such as permissions and recommendations.

The identification of these types of clauses is based on the document "ISO/IEC Directives, Part 2 - Principles and rules of structure and drafting of ISO documents" as well as on a constantly enriched list of verbal forms.

With Requirements, quickly access the main part of the normative text!


What is the Redline format?
New: UPSELL service
Need to identify, monitor and decipher standards?